Key Highlights:
- SlowMist identified malicious JavaScript in two samples associated with Udesk’s customer-service scripts, designed to collect browser-accessible session data and sensitive form submissions.
- The payload can replace cryptocurrency deposit addresses displayed on webpages and alter copied addresses, potentially directing transfers to attacker-controlled destinations.
- SlowMist’s analysis does not establish which platforms served the compromised files, the exposure period or whether any funds were successfully diverted.
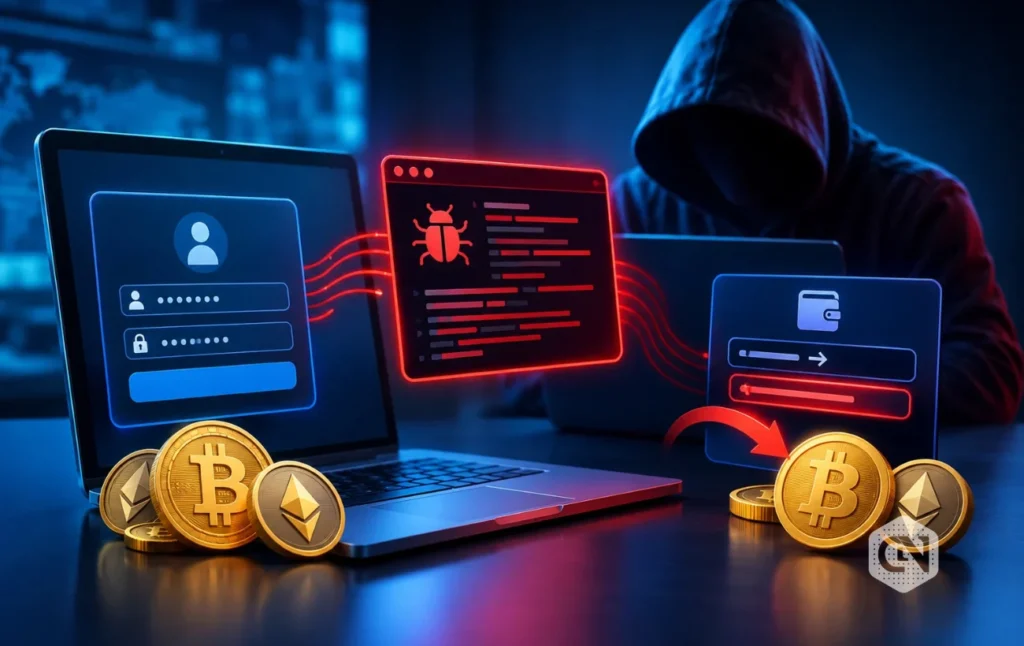
Blockchain security firm SlowMist has identified malicious Javascript injected into scripts associated with Udesk’s customer-service system, warning that the code can expose sensitive user information and interfere with cryptocurrency transfers. The firm exposed two JavaScript samples udeskApi.2026-10-16.cached.js and deeps.js, tracing how a remote script could collect browser data and modify deposit addresses.
The findings point to two distinct risks: stolen login information could enable account or session impersonation, while address substitution could cause users to send funds to an unintended recipient. The report does not confirm that a specific platform was compromised or that any cryptocurrency was stolen.
How Did the Malicious Udesk Scripts Collect User Data?
SlowMist found that the analyzed udeskApi script contained an additional function that decoded a hexadecimal URL and inserted a remote JavaScript file into the webpage. The decoded address pointed to udeskqlobal[.]com/deeps.js, with the domain spelled using the letter “q.” The loader configured the script to execute asynchronously.
Udesk’sdeveloper documentation explains how websites embed its customer-service interface by loading udeskApi.js. SlowMist noted that a chat interface using an iframe does not automatically isolate scripts that execute in the host webpage. A third-party script loaded into that document can access data available to JavaScript in that context, subject to browser security controls.
According to the analysis, deeps.js reads browser-accessible cookies, localStorage and sessionStorage, which may contain session tokens, account information and other data. It also captures non-empty form fields and copies the bodies of certain authentication-related network requests when their URLs match terms such as login, signin, auth, register, signup or password.
SlowMist identified udeskqlobal[.]com/c.php as the data collection endpoint. The script sends information through POST requests and attempts an image-request fallback if transmission encounters an error. The firm warned that reusable session tokens could allow attackers to impersonate logged-in users, while passwords and verification codes submitted through affected pages could expose accounts to further compromise.
The analysis also highlights an important limitation: cookies marked with the HttpOnly attribute cannot be read through the script’s document.cookie access path. However, that protection does not prevent JavaScript from reading other accessible storage or form data. SlowMist further found that data collection and network hooks execute before a hostname check that controls the address-swapping module. As a result, the data-collection risk is not necessarily limited to the three hostname patterns associated with address replacement.
How Can the Payload Replace Crypto Deposit Addresses?
SlowMist found that the payload’s address-manipulation module contains hostname patterns matching mgbx[.]com, bikingexx[.] and bitxex[.]io. The code checks page URLs for terms such as deposit, recharge and assets, then scans webpages for elements containing addresses that match specific character patterns.
When the relevant conditions are met, the script can replace displayed deposit addresses with configured values associated with six labels: BTC, EVM, TRON, Solana, LTC and DOGE. The analysis says the code depends on character patterns and matching order rather than verifying the selected network or an address checksum.
The payload also interferes with clipboard operations. SlowMist identified code that wraps the browser’s Clipboard API< modifies matching copy-button behavior and intercepts certain copy events. Because both the displayed addresses and the copied value can change, comparing the copied address with the address shown on the same webpage may not reveal the substitution.
The clipboard mechanisms have different triggering conditions. In particular, the Clipboard API wrapper is controlled by the hostname configuration and does not need the deposit-page conditions used by other address-replacement functions. SlowMist also found that the script stores the last address it replaced in a shared variable, which can affect what certain copy buttons place on the clipboard.
The firm urged affected website operators to preserve evidence, stop serving suspicious resources and restore trusted script versions. Its recommendations also include revoking potentially exposed sessions, rotating compromised credentials from a clean environment and checking deposit destinations against trusted backend records and transaction histories.
Removing the malicious script alone may not undo hooks and timers that have already been installed in an active page. SlowMist’s analysis therefore recommends investigating the broader exposure, rather than assuming that deleting a script reference resolves every risk. The report does not establish which services actually distributed the analyzed files, how long the code was present, or whether any funds were successfully redirected.